 CloudConsole
AWS KMS request quotas (throttling)
AWS KMS limits cryptographic calls per account per Region. Decrypt, Encrypt, GenerateDataKey, GenerateDataKeyWithoutPlaintext, ReEncrypt, GenerateRandom and the MAC operations share one quota for symmetric keys: 10,000 requests per second by default, 20,000 in Regions such as eu-west-2, eu-central-1 and us-east-2, and 100,000 in us-east-1, us-west-2 and eu-west-1. Calls that AWS services make on your behalf (S3 SSE-KMS, SQS, Secrets Manager, EBS) count too. Over the limit you get ThrottlingException; the quotas are adjustable.
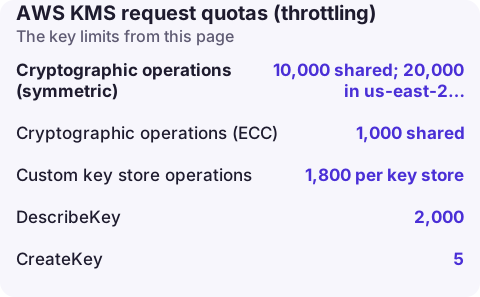
The quotas
| Quota | Default (requests per second) | Applies to |
|---|---|---|
| Cryptographic operations (symmetric) | 10,000 shared; 20,000 in us-east-2, ap-southeast-1, ap-southeast-2, ap-northeast-1, eu-central-1, eu-west-2, eu-south-2; 100,000 in us-east-1, us-west-2, eu-west-1 | Decrypt, Encrypt, GenerateDataKey, GenerateDataKeyWithoutPlaintext, GenerateMac, GenerateRandom, ReEncrypt, VerifyMac |
| Cryptographic operations (ECC) | 1,000 shared | Sign, Verify, DeriveSharedSecret with ECC keys |
| Custom key store operations | 1,800 per key store | Keys in CloudHSM or external key stores (not adjustable) |
| DescribeKey | 2,000 | DescribeKey |
| CreateKey | 5 | CreateKey |
| CreateGrant | 50 | CreateGrant |
Each quota is per account per Region, shared by all keys and all callers. Cross-account use counts against the caller's account, not the key owner's. Resource quotas are separate: 100,000 customer managed keys per Region and 50,000 grants per key by default.
Why you hit it without calling KMS yourself
Integrated services call KMS for you, and those calls use your quota:
- S3 with SSE-KMS: each upload calls GenerateDataKey and each download calls Decrypt. A busy bucket can generate thousands of KMS calls per second. Turning on S3 Bucket Keys reduces this dramatically, because S3 uses a bucket-level key for a period of time instead of calling KMS per object.
- SQS with SSE-KMS: consumers and producers cause GenerateDataKey and Decrypt calls; a longer
KmsDataKeyReusePeriodSeconds(up to 24 hours) cuts them. - Secrets Manager and Parameter Store SecureString: every uncached
GetSecretValueorGetParameter --with-decryptioncauses a Decrypt. Cache secrets in the application. - Lambda environment variables encrypted with a customer managed key are decrypted at cold start.
- DynamoDB, EBS and RDS encryption mostly cache data keys and rarely matter.
What throttling looks like
ThrottlingException: You have exceeded the rate at which you may call KMS.
Reduce the frequency of your calls.
The calling service surfaces this as its own error, usually mentioning KMS throttling, so an S3 upload or SQS send can fail even though the S3 or SQS quotas are nowhere near their limits. CloudTrail records the throttled calls with errorCode: ThrottlingException, which tells you which principal and key are responsible.
Measure and raise
Usage is published to CloudWatch in the AWS/Usage namespace, with Service set to KMS and the operation name as Resource, and the Service Quotas console can create an alarm from it. To see which key and caller dominate:
# Top KMS operations by count, from CloudTrail in the last hour (CloudTrail Lake or Athena are better for volume)
aws cloudtrail lookup-events --lookup-attributes AttributeKey=EventSource,AttributeValue=kms.amazonaws.com \
  --start-time 2026-11-17T08:00:00Z --max-results 50 --query 'Events[].EventName'

aws service-quotas list-service-quotas --service-code kms \
  --query "Quotas[?contains(QuotaName,'Cryptographic')].[QuotaName,QuotaCode,Value]" --output table
Request increases per Region in Service Quotas. Before asking, apply the cheap fixes: Bucket Keys, data key caching (the AWS Encryption SDK supports it), secret caching and SDK retries with backoff.
Questions
What is the KMS request rate limit?
For symmetric keys, cryptographic operations share a quota of 10,000 requests per second by default, 20,000 in some Regions and 100,000 in us-east-1, us-west-2 and eu-west-1. It is per account per Region and adjustable.
Do S3 requests count against the KMS quota?
Yes. With SSE-KMS, S3 calls GenerateDataKey on upload and Decrypt on download on your behalf, and those calls count. S3 Bucket Keys reduce them.
Can KMS quotas be increased?
Yes, all KMS request quotas are adjustable through Service Quotas except the CloudHSM key store quota.
KMS throttling looks like an outage in whatever service sits on top of it, which makes it hard to spot. CloudConsole, a phone app for AWS, is being built to show error alarms and logs from those services on your phone.
About the app → · Download on the App Store