 CloudConsole
AWS errors explained and fixed
What an AWS error message actually means, the usual causes ranked by how often they bite, and the commands that fix them.
138 guides
API Gateway
- 403 Forbidden: User is not authorized to access this resource
- 429 Too Many Requests from API Gateway
- 502 Bad Gateway: Malformed Lambda proxy response
- 504: Endpoint request timed out
- Execution failed due to configuration error: Invalid permissions on Lambda function
- Network error communicating with endpoint
- No 'Access-Control-Allow-Origin' header with API Gateway
- User is not authorized to access this resource with an explicit deny
- {"message":"Missing Authentication Token"}
CloudFormation
- Circular dependency between resources
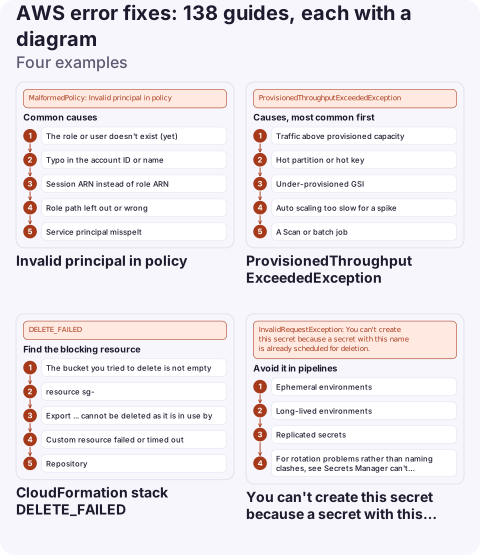
- CloudFormation stack DELETE_FAILED
- Export cannot be deleted as it is in use by another stack
- No updates are to be performed
- Requires capabilities: [CAPABILITY_IAM]
- Resource already exists in stack
- Stack is in ROLLBACK_COMPLETE state and can not be updated
- Stack is in UPDATE_IN_PROGRESS state and can not be updated
- Template format error
- UPDATE_ROLLBACK_FAILED
CloudFront
Credentials, permissions & CLI
- AccessDenied with an explicit deny in a permissions boundary
- AccessDenied with an explicit deny in a service control policy
- AccessDenied: User is not authorized to perform: sts:AssumeRole
- AccessDeniedException: User is not authorized to perform this action because no identity-based policy allows it
- ACM certificate stuck in Pending validation
- AWS.SimpleQueueService.NonExistentQueue: The specified queue does not exist
- Could not connect to the endpoint URL
- denied: Your authorization token has expired. Reauthenticate and try again.
- Error loading SSO Token: Token for <profile> does not exist
- Error when retrieving token from sso: Token has expired and refresh failed
- Error: configuring Terraform AWS Provider: no valid credential sources for Terraform AWS Provider found
- Error: Error acquiring the state lock
- error: You must be logged in to the server (Unauthorized)
- ExpiredToken: The security token included in the request is expired
- failed to assign an IP address to container (Amazon VPC CNI)
- Invalid base64 error when calling aws lambda invoke
- InvalidChangeBatch: Tried to create resource record set but it already exists
- InvalidClientTokenId: The security token included in the request is invalid
- InvalidSignatureException: Signature expired
- KMS AccessDeniedException when reading an encrypted S3 object or secret
- KMSInvalidStateException: key is pending deletion
- MessageRejected: Email address is not verified. The following identities failed the check in region
- name unknown: The repository with name does not exist in the registry with id
- no basic auth credentials when pushing to Amazon ECR
- NodeCreationFailure: Instances failed to join the kubernetes cluster
- NoRegionError: You must specify a region
- Read timeout on endpoint URL
- RequestLimitExceeded: Request limit exceeded (EC2 API)
- ResourceNotFoundException: Secrets Manager can't find the specified secret
- RRSet of type CNAME with DNS name example.com. is not permitted at apex in zone
- SignatureDoesNotMatch: The request signature we calculated does not match the signature you provided
- SSL validation failed for https://... certificate verify failed
- SSM Session Manager: TargetNotConnected
- Step Functions States.Timeout / States.TaskFailed
- The config profile (name) could not be found
- The request must contain the parameter MessageGroupId
- The security token included in the request is invalid
- ThrottlingException: Rate exceeded
- toomanyrequests: You have reached your pull rate limit
- Unable to locate credentials
- Unable to parse config file: ~/.aws/config
- UnauthorizedOperation: You are not authorized to perform this operation. Encoded authorization failure message
- Unknown output type: None
- You can't create this secret because a secret with this name is already scheduled for deletion
DynamoDB
- ConditionalCheckFailedException: The conditional request failed
- ProvisionedThroughputExceededException
- Query condition missed key schema element
- ResourceNotFoundException: Requested resource not found (DynamoDB)
- TransactionCanceledException: Transaction cancelled, please refer cancellation reasons
- ValidationException: Attribute name is a reserved keyword
- ValidationException: Item size has exceeded the maximum allowed size
- ValidationException: The provided key element does not match the schema
EC2
- DependencyViolation: resource has a dependent object
- EC2 Instance Connect: Failed to connect to your instance
- EC2 instance status check failed
- EC2 instance stuck in the stopping state
- EC2 system status check failed
- InsufficientInstanceCapacity: We currently do not have sufficient capacity
- InvalidAMIID.NotFound: The image id does not exist
- InvalidInstanceID.NotFound: The instance ID does not exist
- Permission denied (publickey) when connecting to EC2 over SSH
- ssh: connect to host ec2 port 22: Connection timed out
- VcpuLimitExceeded: You have requested more vCPU capacity than your current vCPU limit
ECS
- CannotPullContainerError: pull image manifest has been retried
- CannotStartContainerError: failed to create task for container
- ECS container exited with exit code 143 (SIGTERM)
- ECS deployment failed: Deployment Circuit Breaker was triggered
- ECS Exec: TargetNotConnectedException when calling the ExecuteCommand operation
- ECS task stopped with exit code 139 (segmentation fault)
- ECS task stopped: Essential container exited with exit code 137
- ECS task stopped: Essential container in task exited with exit code 1
- ECS was unable to assume the role that was provided for this task
- Essential container in task exited
- OutOfMemoryError: Container killed due to memory usage
- ResourceInitializationError: unable to pull secrets or registry auth
- service was unable to place a task because no container instance met all of its requirements
- Task failed container health checks (Amazon ECS)
- Task failed ELB health checks in target group
Lambda
- CodeStorageExceededException: Code storage limit exceeded
- Invalid request provided: Queue visibility timeout is less than Function timeout
- Lambda was unable to configure your environment variables: exceeded the 4KB limit
- Lambda: Task timed out after 3.00 seconds
- RequestEntityTooLargeException: Request must be smaller than 6291456 bytes
- ResourceConflictException: The operation cannot be performed at this time. An update is in progress
- Runtime exited with error: signal: killed (Lambda out of memory)
- Runtime.ExitError: RequestId ... Error: Runtime exited with error
- Runtime.HandlerNotFound: index.handler is undefined or not exported
- Runtime.ImportModuleError: Unable to import module
- Runtime.InvalidEntrypoint
- The provided execution role does not have permissions to call CreateNetworkInterface on EC2
- TooManyRequestsException: Rate Exceeded (Lambda throttling)
- Unzipped size must be smaller than 262144000 bytes
Load balancers
RDS
S3
- AccessControlListNotSupported: The bucket does not allow ACLs
- AccessDenied: Request has expired (presigned URL)
- An error occurred (403) when calling the HeadObject operation: Forbidden
- AuthorizationHeaderMalformed: the region 'us-east-1' is wrong; expecting 'eu-west-2'
- BucketAlreadyExists: The requested bucket name is not available
- BucketNotEmpty: The bucket you tried to delete is not empty
- Invalid principal in policy
- InvalidAccessKeyId: The AWS Access Key Id you provided does not exist in our records
- InvalidObjectState: The operation is not valid for the object's storage class
- NoSuchBucket: The specified bucket does not exist
- NoSuchKey: The specified key does not exist
- PermanentRedirect: The bucket you are attempting to access must be addressed using the specified endpoint
- S3 AccessDenied: Access Denied when calling an S3 operation
- SlowDown: Please reduce your request rate (503)
- Unable to validate the following destination configurations