 CloudConsole
IAM policy examples, least privilege
Copy-paste IAM policies for everyday jobs, scoped to least privilege, with what each statement allows and the mistakes to avoid.
40 guides
- ABAC: tag-based access control policy example
- CodeBuild service role permissions
- Cross-account assume role with an external ID
- Deny all regions except approved ones (aws:RequestedRegion)
- ECS task role vs task execution role
- EKS IRSA: IAM role trust policy for a service account
- GitHub Actions OIDC: IAM role trust policy
- IAM permissions boundary: let developers create roles safely
- IAM policy: CloudWatch read-only for a monitoring tool
- IAM policy: Cost Explorer read-only
- IAM policy: deny deleting critical resources
- IAM policy: deny requests from outside approved IP addresses
- IAM policy: invoke one Amazon Bedrock model
- IAM policy: kms:Decrypt on one key
- IAM policy: Lambda reading from an SQS queue
- IAM policy: push and pull one ECR repository
- IAM policy: RDS IAM database authentication
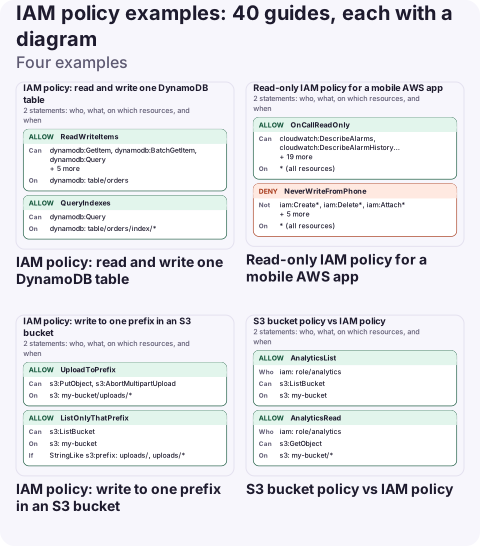
- IAM policy: read and write one DynamoDB table
- IAM policy: read one secret from Secrets Manager
- IAM policy: read Parameter Store parameters under a path
- IAM policy: read-only access to a single S3 bucket
- IAM policy: require MFA for IAM users
- IAM policy: Session Manager access to tagged instances
- IAM policy: start and stop EC2 instances by tag
- IAM policy: users manage their own credentials and MFA
- IAM policy: write to one CloudWatch Logs log group
- IAM policy: write to one prefix in an S3 bucket
- IAM role for an EC2 instance to access S3
- IAM role trust policy: examples and how it works
- iam:PassRole: policy example and why it matters
- KMS key policy: a working example explained
- Lambda execution role: trust policy and basic permissions
- Read-only IAM policy for a mobile AWS app
- ReadOnlyAccess vs ViewOnlyAccess (and SecurityAudit)
- S3 bucket policy vs IAM policy
- S3 bucket policy: deny requests that are not over HTTPS
- S3 bucket policy: require SSE-KMS encryption on uploads
- S3 bucket policy: restrict access to a VPC endpoint
- SCP: deny all actions by the root user
- SCP: deny leaving the organisation