 CloudConsole
CloudFront returns AccessDenied from an S3 origin (OAC / OAI)
CloudFront passes S3's XML AccessDenied straight through when the bucket won't serve the request. With origin access control (OAC), the bucket policy must allow the cloudfront.amazonaws.com service principal to s3:GetObject with an AWS:SourceArn condition matching your distribution's ARN. If that's in place, the usual causes are a missing default root object, a path that doesn't exist (S3 returns 403 for missing keys), an S3 website endpoint used as the origin, or SSE-KMS objects the key policy doesn't let CloudFront decrypt.
What you see
A browser or curl to your distribution returns HTTP 403 with S3's own body:
<Error><Code>AccessDenied</Code><Message>Access Denied</Message>
<RequestId>…</RequestId><HostId>…</HostId></Error>
Because this body comes from S3, CloudFront reached the origin; the bucket refused. (If you see a CloudFront-branded "The request could not be satisfied" page instead, the problem is between viewer and CloudFront or CloudFront and origin; see that error.)
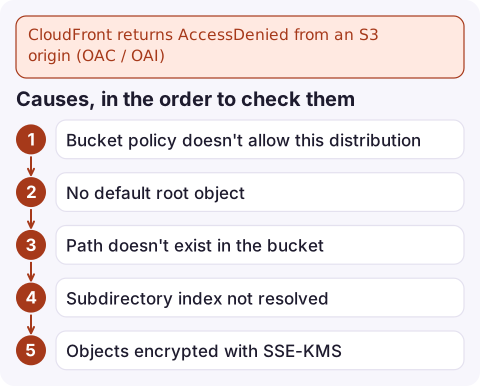
Causes, in the order to check them
| Cause | Clue |
|---|---|
| Bucket policy doesn't allow this distribution | Every path fails, including files you know exist |
| No default root object | /index.html works, / returns 403 |
| Path doesn't exist in the bucket | Some URLs fail; often SPA routes like /settings or /blog/post/ |
| Subdirectory index not resolved | /docs/ fails although docs/index.html exists; the default root object applies only to the root |
| Objects encrypted with SSE-KMS | Newly uploaded files fail after a bucket encryption change |
| Origin is the S3 website endpoint | Origin domain contains s3-website; OAC/OAI don't apply to website endpoints |
| Legacy OAI removed or not referenced in the policy | Distribution was migrated to OAC but the policy still names the OAI, or the reverse |
Fix the bucket policy for OAC
Get the distribution ARN, then allow it in the bucket policy:
aws cloudfront get-distribution --id E1A2B3C4D5E6F7 --query Distribution.ARN --output text{
"Version": "2012-10-17",
"Statement": [{
"Sid": "AllowCloudFrontOAC",
"Effect": "Allow",
"Principal": { "Service": "cloudfront.amazonaws.com" },
"Action": "s3:GetObject",
"Resource": "arn:aws:s3:::my-site-bucket/*",
"Condition": { "StringEquals": {
"AWS:SourceArn": "arn:aws:cloudfront::123456789012:distribution/E1A2B3C4D5E6F7" } }
}]
}aws s3api put-bucket-policy --bucket my-site-bucket --policy file://policy.jsonCheck the origin really uses OAC and the REST endpoint (my-site-bucket.s3.eu-west-2.amazonaws.com), not the website endpoint:
aws cloudfront get-distribution-config --id E1A2B3C4D5E6F7 \
  --query 'DistributionConfig.Origins.Items[].[DomainName,OriginAccessControlId]'
Other fixes
- Root path: set the distribution's default root object to
index.html. - Single-page apps: add custom error responses that map 403 (and 404) to
/index.htmlwith status 200, so client-side routes load. - Want real 404s for missing files instead of 403? Also grant the CloudFront principal
s3:ListBucketon the bucket ARN; S3 then reports missing keys as 404. - Subdirectory indexes: rewrite
/path/to/path/index.htmlwith a CloudFront Function on viewer requests. - SSE-KMS: OAC can read KMS-encrypted objects if the key policy allows the CloudFront service principal
kms:Decryptwith the sameAWS:SourceArncondition. OAI cannot.
After fixing
CloudFront may have cached the 403. Error responses are cached for a short time by default, so either wait or invalidate the affected paths (see invalidating the CloudFront cache); you can also lower the error caching minimum TTL for 403 in the distribution's error pages settings. Then test with curl -I and look for x-cache: Miss from cloudfront followed by a 200.
Questions
Why does CloudFront return access denied with OAC?
Most often the bucket policy doesn't allow the cloudfront.amazonaws.com principal with an AWS:SourceArn condition matching this exact distribution, or the request is for a path that doesn't exist in the bucket.
Why does my CloudFront S3 site return 403 on refresh?
The browser requests a client-side route such as /dashboard, which isn't an object in the bucket. Configure custom error responses that return /index.html for 403 and 404.
Can I use OAC with an S3 website endpoint?
No. OAC and OAI only work with the S3 REST endpoint. A website endpoint origin is treated as a custom origin and needs public objects.

A site returning 403 to every visitor is the kind of outage you hear about from customers first. CloudFront 4xx and 5xx error-rate alarms help; CloudConsole, a phone app for AWS, is built to show those alarms and the distribution's state on your phone.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store