 CloudConsole
Unable to validate the following destination configurations
When you save an S3 event notification, S3 checks that it can deliver to every destination in the bucket's whole notification configuration. The error means at least one destination fails that check: the Lambda function's resource policy doesn't let s3.amazonaws.com invoke it, the SNS topic or SQS queue policy doesn't allow S3 to publish, the topic or queue is encrypted with an AWS managed KMS key, or an older notification points at a target that no longer exists.
Read the error
An error occurred (InvalidArgument) when calling the PutBucketNotificationConfiguration operation:
Unable to validate the following destination configurations
S3 validates the full configuration, not just the notification you're adding. If someone deleted a queue last year that an old notification still points at, every future change to that bucket's notifications fails until the stale entry is removed. List what's there first:
aws s3api get-bucket-notification-configuration --bucket my-bucketCauses and fixes by destination
| Destination | Fix |
|---|---|
| Lambda | Add a resource-based permission for s3.amazonaws.com scoped to the bucket (command below). Adding the trigger in the Lambda console does this for you; CloudFormation and Terraform don't. |
| SNS topic | Topic policy must allow SNS:Publish for principal s3.amazonaws.com, with aws:SourceArn set to the bucket ARN. |
| SQS queue | Queue policy must allow SQS:SendMessage for s3.amazonaws.com, conditioned on the bucket ARN. FIFO queues aren't supported as S3 notification targets. |
| Encrypted topic/queue | The AWS managed keys aws/sns and aws/sqs can't be used. Use a customer managed key whose key policy lets s3.amazonaws.com use kms:GenerateDataKey and kms:Decrypt. |
| Stale target | Remove notifications pointing at deleted functions, topics or queues. |
Fix a Lambda destination
aws lambda add-permission \
  --function-name thumbnailer \
  --statement-id s3-my-bucket \
  --action lambda:InvokeFunction \
  --principal s3.amazonaws.com \
  --source-arn arn:aws:s3:::my-bucket \
  --source-account 123456789012

# Confirm
aws lambda get-policy --function-name thumbnailer --query Policy --output text
If the notification targets an alias or version (thumbnailer:live), add the permission with --qualifier live too; the permission is per qualifier.
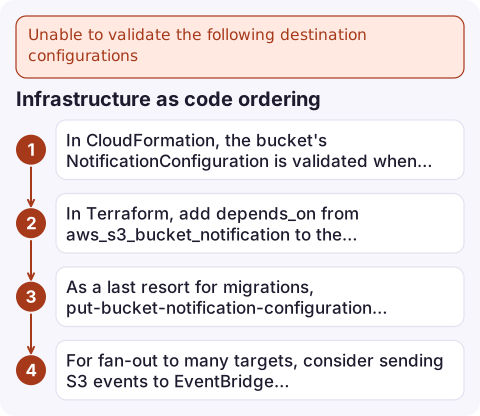
Infrastructure as code ordering
- In CloudFormation, the bucket's
NotificationConfigurationis validated when the bucket is created or updated. AddDependsOnon theAWS::Lambda::Permissionor queue/topic policy so it exists first. If that creates a circular dependency, build the bucket name yourself instead of referencing the bucket's ARN. - In Terraform, add
depends_onfromaws_s3_bucket_notificationto the permission or policy. - As a last resort for migrations,
put-bucket-notification-configurationaccepts--skip-destination-validation, but events to a broken target are then silently lost. - For fan-out to many targets, consider sending S3 events to EventBridge instead of maintaining per-target policies.
Questions
How do I fix unable to validate the following destination configurations for S3 to Lambda?
Run aws lambda add-permission with principal s3.amazonaws.com and the bucket ARN as source-arn, then save the notification again.
Why does adding an S3 notification to SNS or SQS fail validation?
The topic or queue policy doesn't allow S3 to publish, or it's encrypted with the AWS managed aws/sns or aws/sqs key, which S3 can't use.
Why does the error appear when I only changed a different notification?
S3 validates every destination in the bucket's configuration. Remove any notification whose target was deleted.

A silently missing notification shows up later as work that never happened. CloudConsole, a phone app for AWS, is being built to show Lambda and queue metrics with alarms on your phone, so a pipeline that has gone quiet is easier to notice.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store