 CloudConsole
ap-east-1: Asia Pacific (Hong Kong)
ap-east-1 is the code for the Asia Pacific (Hong Kong) region. It is an opt-in region that must be enabled per account, and it serves users and businesses in Hong Kong and the surrounding area. It is part of the standard AWS partition, which is not the same thing as the AWS China regions in Beijing and Ningxia.
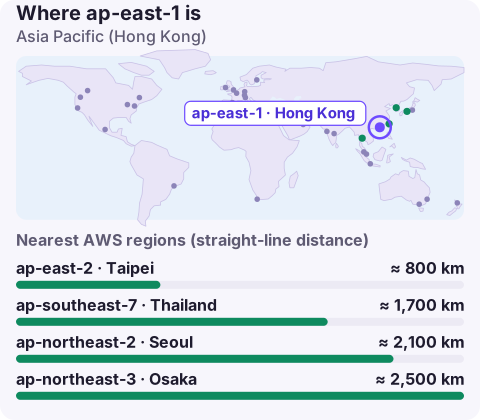
What ap-east-1 is for
- Hong Kong users and businesses: banks, trading firms, logistics and consumer apps with Hong Kong customers get local hosting and short round trips.
- Financial services: Hong Kong's financial regulators expect firms to manage outsourcing and data-location risks carefully; hosting locally simplifies that conversation. Read the guidance that applies to you rather than assuming a region settles it.
- Southern China proximity: for services reaching users in the Pearl River Delta from outside mainland China, Hong Kong is geographically close, though routing across the boundary varies.
Hong Kong is not AWS China
This trips up many teams. ap-east-1 is a normal AWS region: same accounts, same IAM, same console, ARNs starting arn:aws:. The mainland China regions (cn-north-1 Beijing and cn-northwest-1 Ningxia) are a separate partition, aws-cn, with separate accounts and credentials, operated by local partners. If your goal is to serve users inside mainland China from mainland infrastructure, Hong Kong isn't a substitute; you'd need AWS China accounts and the licensing that goes with them, such as an ICP filing for public websites.
Enabling ap-east-1
aws account get-region-opt-status --region-name ap-east-1
aws account enable-region --region-name ap-east-1

# once ENABLED
aws ec2 describe-availability-zones --region ap-east-1 \
  --query 'AvailabilityZones[].[ZoneName,ZoneId]' --output table
Hong Kong was one of the first regions launched under the opt-in model, so it's a frequent source of "why can't I see it in the console?" questions. In an organisation, enable it from the management account with --account-id and allow it in any region-restricting SCP.
Targeting Hong Kong from tools
Use --region ap-east-1, AWS_REGION=ap-east-1, or the profile setting. Endpoints follow <service>.ap-east-1.amazonaws.com. The code is easy to confuse with ap-east-2 (Taipei) and ap-southeast-1 (Singapore); name profiles after the city to avoid mistakes.
If calls fail with an invalid security token right after enabling, the credentials were likely issued by the global STS endpoint, whose tokens by default don't work in opt-in regions. Use regional STS or change the global endpoint token setting in IAM.
Neighbours and recovery
| Region | Why consider it |
|---|---|
| ap-southeast-1 (Singapore) | Large South-East Asian hub; enabled by default |
| ap-east-2 (Taipei) | Very close geographically; opt-in |
| ap-northeast-1 (Tokyo) | Broad catalogue, common DR target |
Check service availability in both your primary and recovery regions on the AWS Regional Services List; newer services can reach Singapore or Tokyo before Hong Kong.
If your recovery plan copies data from Hong Kong to Singapore or Tokyo, confirm first that regulators and customer contracts permit storage outside Hong Kong; a backup that breaks a data-location promise is a problem you discover in an audit, not an outage.
Questions
Is ap-east-1 enabled by default?
No. Hong Kong is an opt-in region. Enable it in the account settings or with aws account enable-region.
Is ap-east-1 the same as AWS China?
No. ap-east-1 is in the standard AWS partition. The mainland China regions use a separate aws-cn partition with separate accounts.
Where is ap-east-1?
In Hong Kong.
If you run in Hong Kong and somewhere else in Asia, you need both regions' alarms in view. CloudConsole, a phone app for AWS, is built to show alarms and resources across regions on your phone.
About the app → · Download on the App Store