 CloudConsole
{"message":"Missing Authentication Token"}
Despite its name, this 403 from a REST API usually means the path or method you called does not exist in the deployed stage: a missing stage name in the URL, a typo, a method that was never deployed, or the wrong HTTP verb. Only when the method really uses IAM authorisation does it mean the request was not signed.
Why the message is misleading
When a request arrives at a REST API, API Gateway looks for a matching resource and method in the stage. If nothing matches, it cannot tell whether you asked for something that does not exist or something you are not allowed to see, so it returns the same response it uses for unauthenticated requests:
HTTP/1.1 403 Forbidden
x-amzn-ErrorType: MissingAuthenticationTokenException

{"message":"Missing Authentication Token"}
So treat it first as "404 Not Found". HTTP APIs behave differently and return {"message":"Not Found"} with a 404 for unmatched routes.
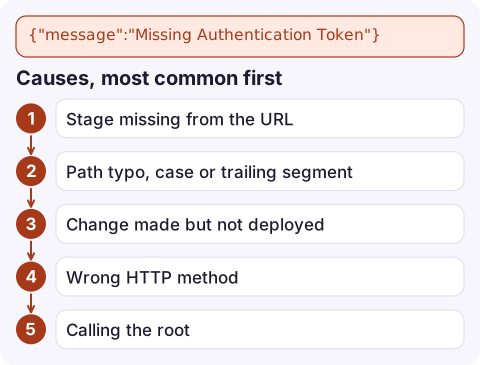
Causes, most common first
| Cause | Example |
|---|---|
| Stage missing from the URL | https://abc123.execute-api.eu-west-2.amazonaws.com/orders instead of .../prod/orders |
| Path typo, case or trailing segment | /Orders, /order, /orders/42/ when only /orders/{id} exists |
| Change made but not deployed | Method works in the console's Test tab but not from curl |
| Wrong HTTP method | Sending GET to a resource that only has POST |
| Calling the root | Opening the stage URL in a browser when / has no method |
| IAM-authorised method called without SigV4 | Method's authorisation type is AWS_IAM and the request has no signature |
Check what is actually deployed
List the API's resources and methods:
aws apigateway get-resources --rest-api-id abc123 \
  --query 'items[].{path:path,methods:resourceMethods}'
List stages and when each was last deployed:
aws apigateway get-stages --rest-api-id abc123 \
  --query 'item[].{stage:stageName,deployment:deploymentId,updated:lastUpdatedDate}'
Then call the exact URL with the exact method and look at the response headers:
curl -i -X GET https://abc123.execute-api.eu-west-2.amazonaws.com/prod/orders/42If you use a custom domain, also check the base path mapping: a mapping of api to stage prod means the public URL is https://example.com/api/orders/42, without the stage name.
Fix it
- Correct the URL: include the stage (or the custom domain's base path) and match the path exactly, including case.
- Deploy the API after any change to resources, methods or integrations. Console edits do nothing for clients until deployed:
aws apigateway create-deployment --rest-api-id abc123 \ --stage-name prod --description "add GET /orders/{id}" - Add the missing method if the verb is genuinely unsupported, or add a
{proxy+}resource withANYif your backend does its own routing. - Sign IAM requests with SigV4. With curl 7.75 or later:
curl --aws-sigv4 "aws:amz:eu-west-2:execute-api" \
  --user "$AWS_ACCESS_KEY_ID:$AWS_SECRET_ACCESS_KEY" \
  -H "x-amz-security-token: $AWS_SESSION_TOKEN" \
  https://abc123.execute-api.eu-west-2.amazonaws.com/prod/orders/42
Make it less confusing for clients
You can change what API Gateway returns for this case by editing the MISSING_AUTHENTICATION_TOKEN gateway response, for example to a 404, then redeploying:
aws apigateway update-gateway-response --rest-api-id abc123 \
  --response-type MISSING_AUTHENTICATION_TOKEN \
  --patch-operations op=replace,path=/statusCode,value=404
Browsers calling a wrong path often report it as a CORS error, because gateway responses carry no CORS headers by default; see API Gateway CORS errors.
Questions
Why does API Gateway say Missing Authentication Token when my API has no auth?
Because the requested path or method does not exist in the deployed stage. API Gateway returns this 403 for any unmatched route on a REST API.
Do I need to redeploy after changing an API Gateway method?
Yes, for REST APIs. Changes stay in the draft until you create a deployment for the stage. HTTP APIs can auto-deploy if the stage has auto-deploy turned on.
How do I call an API Gateway endpoint that uses IAM authorisation?
Sign the request with SigV4 for the execute-api service, using an SDK, a signing library, or curl's --aws-sigv4 option.

A spike of 403s right after a release often means a route was renamed or not deployed. CloudConsole, a phone app for AWS, is built to show API error alarms and the related logs on your phone, so you can link the spike to the change.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store