 CloudConsole
ResourceNotFoundException: Secrets Manager can't find the specified secret
Secrets Manager has no secret matching that name or ARN in the Region and account you called. Usually the client is in a different Region from the secret (they are Regional), the name is slightly different, or the secret was deleted. A variant mentioning a staging label means the secret exists but has no version with that label.
What it looks like
An error occurred (ResourceNotFoundException) when calling the GetSecretValue
operation: Secrets Manager can't find the specified secret.
The variant Secrets Manager can't find the specified secret value for staging label: AWSPENDING means the secret exists but no version carries that label, usually during or after an interrupted rotation. A missing permission produces AccessDeniedException instead, so this error tells you the request was allowed but the lookup failed.
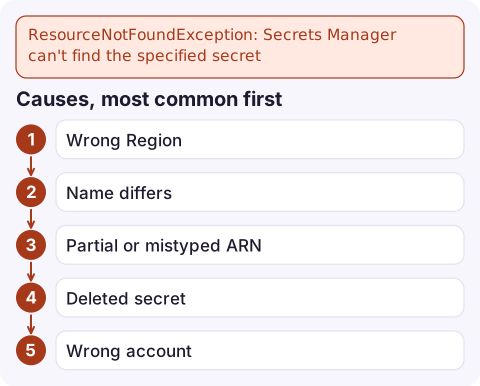
Causes, most common first
- Wrong Region. Secrets exist in one Region unless replicated. A secret in
eu-west-2is invisible to a client configured foreu-west-1. - Name differs. Names are case-sensitive, and path-like names (
prod/orders/db) are easy to get slightly wrong between environments. - Partial or mistyped ARN. Secret ARNs end in a hyphen and six random characters. A full ARN with the wrong suffix fails; for other accounts' secrets you must use the full ARN.
- Deleted secret. A secret scheduled for deletion fails differently (it is "marked for deletion") until the recovery window ends; after that it is gone.
- Wrong account or credentials resolving to a different profile.
Diagnose
List secrets by name prefix in the Region you expect, including ones pending deletion:
aws secretsmanager list-secrets --region eu-west-2 \
  --filters Key=name,Values=prod/orders \
  --include-planned-deletion \
  --query 'SecretList[].[Name,ARN,DeletedDate]' --output table
Describe the secret to see its versions and staging labels:
aws secretsmanager describe-secret --secret-id prod/orders/db --region eu-west-2 \
  --query '{arn:ARN,versions:VersionIdsToStages,rotation:RotationEnabled,replicas:ReplicationStatus[].Region}'
If the secret appears in neither Region you checked, look across Regions or in CloudTrail for DeleteSecret.
Fix it
- Set the Region explicitly on the client, or replicate the secret to the Regions that read it.
- Use the secret's full ARN in IAM policies, ECS task definitions and cross-account access; use the name in same-account application code if you prefer.
- Restore a secret scheduled for deletion within its recovery window:
aws secretsmanager restore-secret --secret-id prod/orders/db --region eu-west-2 - Fix staging labels after a failed rotation: confirm a version holds
AWSCURRENT, then let rotation retry or move the label withupdate-secret-version-stage. - ECS: a wrong secret ARN in a task definition stops the task at start-up; see ResourceInitializationError.
Mistakes to avoid
- Recreating a secret with the same name and assuming its ARN is unchanged. The random suffix is new, so policies and task definitions using the old full ARN break.
- Fetching secrets on every request with no caching; use a caching client or the Lambda extension, which also reduces API calls when a secret is missing.
- Logging the secret value while debugging this error. Log the name, Region and ARN only.
Questions
Is AWS Secrets Manager Regional?
Yes. Each secret lives in one Region unless you configure replication. Clients must call the Region where the secret, or a replica, exists.
How do I get a secret from Secrets Manager in eu-west-2 with the CLI?
Run aws secretsmanager get-secret-value --secret-id with the name or ARN and --region eu-west-2, adding --query SecretString --output text for just the value.
Can I recover a deleted secret?
Only during its recovery window (7 to 30 days, set when deleting), using restore-secret. After the window ends the secret is permanently deleted.

When an application cannot read its database secret, every request fails at once. CloudConsole, a phone app for AWS, is built to show those error alarms and the log lines behind them on your phone so the cause is clear quickly.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store