 CloudConsole
IAM policy: read and write one DynamoDB table
Allow the item-level actions your code uses (GetItem, PutItem, UpdateItem, DeleteItem, Query and the batch calls) on the table ARN, and add the table's index ARN (table/orders/index/*) for queries on secondary indexes. Leave out Scan, DeleteTable and UpdateTable unless the app really needs them.
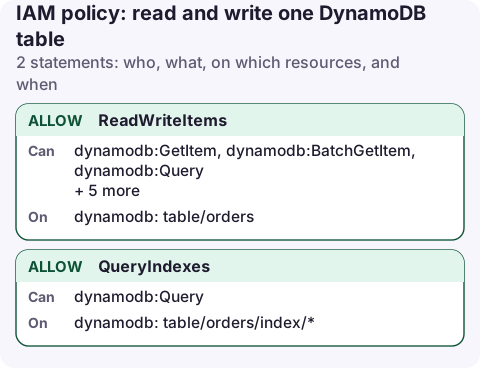
The policy
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "ReadWriteItems",
      "Effect": "Allow",
      "Action": [
        "dynamodb:GetItem",
        "dynamodb:BatchGetItem",
        "dynamodb:Query",
        "dynamodb:PutItem",
        "dynamodb:UpdateItem",
        "dynamodb:DeleteItem",
        "dynamodb:BatchWriteItem",
        "dynamodb:ConditionCheckItem"
      ],
      "Resource": "arn:aws:dynamodb:eu-west-2:123456789012:table/orders"
    },
    {
      "Sid": "QueryIndexes",
      "Effect": "Allow",
      "Action": "dynamodb:Query",
      "Resource": "arn:aws:dynamodb:eu-west-2:123456789012:table/orders/index/*"
    }
  ]
}
What each part covers
- Reads:
GetItemandBatchGetItemfor single keys,Queryfor a partition. - Writes:
PutItem,UpdateItem,DeleteItemandBatchWriteItem.ConditionCheckItemis only used inside transactions. - Transactions have no permission of their own.
TransactWriteItemsis authorised as the individual put, update, delete and condition-check actions;TransactGetItemsasGetItem. - QueryIndexes: global and local secondary indexes are separate resources. A
QuerywithIndexNameis checked againsttable/orders/index/<name>, so the table ARN alone isn't enough.
Scan is left out on purpose. It reads the whole table, costs accordingly, and is rarely what request-path code should do. Add it only for jobs that need it.
Attach it
aws iam put-role-policy --role-name orders-api-lambda \
  --policy-name orders-table --policy-document file://orders-table.json

aws iam simulate-principal-policy \
  --policy-source-arn arn:aws:iam::123456789012:role/orders-api-lambda \
  --action-names dynamodb:Query dynamodb:Scan \
  --resource-arns arn:aws:dynamodb:eu-west-2:123456789012:table/orders
The simulator should show allowed for Query and implicitDeny for Scan.
Variations
- Read-only: keep
GetItem,BatchGetItem,QueryandDescribeTable. - Each user sees only their own items: add
"Condition": {"ForAllValues:StringEquals": {"dynamodb:LeadingKeys": ["${aws:PrincipalTag/customer_id}"]}}, so requests may only use partition keys equal to the caller's tag. This is how mobile apps with Cognito identities are commonly scoped. - Streams consumer: add
dynamodb:DescribeStream,dynamodb:GetRecords,dynamodb:GetShardIteratorontable/orders/stream/*anddynamodb:ListStreams. - PartiQL:
ExecuteStatementis authorised asdynamodb:PartiQLSelect,PartiQLInsert,PartiQLUpdateandPartiQLDelete.
Find every action your code calls
If you're tightening an existing broad policy, look at what the role really does before trimming. With CloudTrail data events enabled for the table, item-level calls appear as events; IAM Access Analyzer can also generate a policy from a role's CloudTrail history. Last-accessed information shows which services a role has used, but not which DynamoDB actions.
aws iam generate-service-last-accessed-details \
  --arn arn:aws:iam::123456789012:role/orders-api-lambda
Common mistakes
- Index queries denied while table queries work: the
/index/*resource is missing. - Wrong region or account in the ARN. Table ARNs are regional; a global table needs the ARN for each replica region the app writes to.
dynamodb:*on*in production: includesDeleteTableand backup deletion. If you need a safety net, see deny deleting a resource.- Customer managed KMS key on the table: also allow
kms:Decrypton it, or reads fail with a KMS access error.
Questions
What is the minimum IAM policy for DynamoDB Query?
dynamodb:Query on the table ARN, and on table/<name>/index/* if you query an index.
Do DynamoDB transactions need a separate permission?
No. Each item in a transaction is checked against the matching item action, such as PutItem or ConditionCheckItem.
If writes to a table start failing, throttling and access errors look similar from the outside. Checking the table's metrics and the function's logs from your phone tells you which one it is.
About the app → · Download on the App Store