 CloudConsole
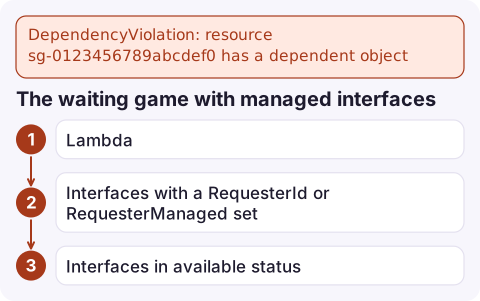
DependencyViolation: resource has a dependent object
EC2 won't delete a security group, subnet, VPC or gateway while something still uses it. For security groups that means network interfaces attached to it (from instances, Lambda, RDS, load balancers, VPC endpoints, EKS) or rules in other groups that reference it. For VPCs and subnets it means anything still inside them. Find the dependents with describe-network-interfaces and the filters below, remove them, then delete again.
Messages you'll see
An error occurred (DependencyViolation) when calling the DeleteSecurityGroup operation:
resource sg-0123456789abcdef0 has a dependent object

An error occurred (DependencyViolation) when calling the DeleteVpc operation:
The vpc 'vpc-0a1b2c3d4e5f60718' has dependencies and cannot be deleted.

An error occurred (DependencyViolation) when calling the DeleteSubnet operation:
The subnet 'subnet-0a1b2c3d4e5f60718' has dependencies and cannot be deleted.
It also appears inside CloudFormation DELETE_FAILED events and Terraform destroys, often after a long retry loop.
Security group: find what uses it
# Network interfaces using the group (instances, Lambda, RDS, ELB, endpoints...)
aws ec2 describe-network-interfaces \
  --filters Name=group-id,Values=sg-0123456789abcdef0 \
  --query 'NetworkInterfaces[].[NetworkInterfaceId,InterfaceType,Description,Attachment.InstanceId,RequesterId]' \
  --output table

# Other groups with rules that reference it
aws ec2 describe-security-groups \
  --filters Name=ip-permission.group-id,Values=sg-0123456789abcdef0 \
  --query 'SecurityGroups[].[GroupId,GroupName]'
aws ec2 describe-security-groups \
  --filters Name=egress.ip-permission.group-id,Values=sg-0123456789abcdef0 \
  --query 'SecurityGroups[].[GroupId,GroupName]'
The interface Description usually names the owner: AWS Lambda VPC ENI-..., ELB app/..., RDSNetworkInterface, VPC Endpoint Interface vpce-.... Change the owning resource to use a different group (or delete it); then remove referencing rules with revoke-security-group-ingress/-egress. A security group also can't be deleted while it's a VPC's default group.
VPC or subnet: what's still inside
Before delete-vpc works, remove (roughly in this order): instances and load balancers, NAT gateways (and release their Elastic IPs), VPC endpoints, Lambda VPC configuration, RDS/ElastiCache subnet groups, Transit Gateway or peering attachments, detached and deleted internet gateways, non-default subnets, route tables, network ACLs and security groups. List leftover interfaces in the VPC:
aws ec2 describe-network-interfaces --filters Name=vpc-id,Values=vpc-0a1b2c3d4e5f60718 \
  --query 'NetworkInterfaces[].[NetworkInterfaceId,InterfaceType,Description,Status]' --output table
The console's Delete VPC action removes many of these for you and lists the ones it can't.
The waiting game with managed interfaces
- Lambda interfaces are released only after no function uses that subnet and security group combination; after removing VPC config or deleting functions it can take a while (sometimes much longer than you'd expect). Don't delete them by hand while in use; wait and retry.
- Interfaces with a
RequesterIdorRequesterManagedset belong to an AWS service and can't be detached or deleted by you; delete the owning resource. - Interfaces in
availablestatus owned by you are leftovers and can be deleted withaws ec2 delete-network-interface.
Questions
How do I find what is using a security group?
Run aws ec2 describe-network-interfaces with the filter group-id set to the group, and describe-security-groups with ip-permission.group-id to find rules in other groups that reference it.
Why can't I delete my VPC?
Something is still inside it: network interfaces, NAT gateways, endpoints, gateways, subnets or security groups. List network interfaces filtered by vpc-id to find them.
How long does it take for Lambda network interfaces to be deleted?
Lambda releases them once no function uses that subnet and security group combination; it can take a significant time. Retry the delete later rather than removing them manually.

Teardowns that hang on dependencies tend to fail late in a pipeline. CloudConsole, a phone app for AWS, is being built to show resources and alarms on your phone, so you can check what is still running in a VPC from anywhere.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store