 CloudConsole
InvalidClientTokenId: The security token included in the request is invalid
InvalidClientTokenId means STS or IAM does not recognise the access key ID you signed with, or the session token sent with it. In Terraform it almost always appears during provider start-up, when the provider calls sts:GetCallerIdentity with credentials from an unexpected source; check which credentials Terraform resolves (environment variables beat profiles) and whether the key is still active.
Where you see it
InvalidClientTokenId is the error code STS and IAM use for unrecognised credentials. The Terraform AWS provider validates credentials as soon as it starts, by calling GetCallerIdentity, so a bad key stops plan before anything is read:
Error: configuring Terraform AWS Provider: validating provider credentials:
retrieving caller identity from STS: operation error STS: GetCallerIdentity,
https response error StatusCode: 403, RequestID: 6f0e…,
api error InvalidClientTokenId: The security token included in the request is invalid.
The same code appears from the CLI (aws sts get-caller-identity and IAM commands) and from EC2 or CloudFormation APIs in some cases. It is an authentication failure, not a missing permission.
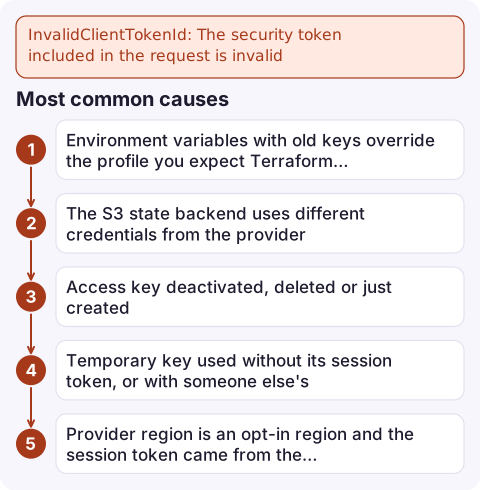
Most common causes
| Cause | Check |
|---|---|
| Environment variables with old keys override the profile you expect Terraform to use | env | grep '^AWS_' in the shell or CI job that runs Terraform |
| The S3 state backend uses different credentials from the provider | Error appears during terraform init, not plan; the backend "s3" block has its own profile/role settings |
| Access key deactivated, deleted or just created | New keys can take a few seconds to be accepted everywhere; a deleted key never will |
| Temporary key used without its session token, or with someone else's | Key ID starts with ASIA but AWS_SESSION_TOKEN is empty or from an earlier session |
| Provider region is an opt-in region and the session token came from the global STS endpoint | Fails only for providers aliased to regions such as af-south-1 or ap-east-1 |
Fix it step by step
- Reproduce outside Terraform using exactly the same environment:
If the CLI fails too, the credentials are the problem, not your HCL.aws sts get-caller-identity aws configure list - Remove the conflicting source. Unset stale variables, or point Terraform at a profile explicitly:
unset AWS_ACCESS_KEY_ID AWS_SECRET_ACCESS_KEY AWS_SESSION_TOKEN export AWS_PROFILE=prod-admin terraform plan - Check the key status from an identity that works:
aws iam list-access-keys --user-name terraform-ci \ --query 'AccessKeyMetadata[].[AccessKeyId,Status,CreateDate]' --output table - Fix the backend separately if
initfails: give thebackend "s3"block the same profile or role, then re-runterraform init -reconfigure. - Opt-in regions: set the IAM global endpoint token version to v2 in account settings, or have your role-assumption step use a regional STS endpoint.
CI-specific gotchas
- A pipeline migrated from stored keys to OIDC role assumption may still inject the old secret variables. Whichever source the SDK finds first wins, and environment variables come first.
- Masked secrets sometimes pick up a trailing newline or space when pasted into a CI settings page. That produces this error for the access key ID, or SignatureDoesNotMatch if only the secret is damaged.
- Never set
skip_credentials_validation = trueto make the error go away; the first real API call will fail with the same message, just later and less clearly.
How this differs from similar errors
ExpiredToken means the credentials were valid and have run out; InvalidClientTokenId means AWS does not recognise them at all. InvalidAccessKeyId is S3's equivalent wording. AccessDenied means authentication succeeded and a policy blocked the action, which is a different fix entirely.
Questions
Why does Terraform say InvalidClientTokenId when the CLI works?
Terraform is resolving different credentials, usually from environment variables, a different profile, or the S3 backend's own settings. Run Terraform and the CLI from the same shell with AWS_PROFILE set explicitly.
Can a newly created access key cause InvalidClientTokenId?
Briefly, yes: IAM changes are eventually consistent, so a key used within seconds of creation can be rejected. If the error persists after a minute, the key or its secret is wrong.
Is InvalidClientTokenId a permissions problem?
No. It is returned before any policy is evaluated. Adding IAM permissions will not fix it; fixing the credentials will.

When a pipeline breaks on this error, you usually find out from a failed deploy notification. CloudConsole, a phone app for AWS, is built to show alarms and resource state on your phone, which helps you judge whether the failed deploy left anything half-changed.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store