 CloudConsole
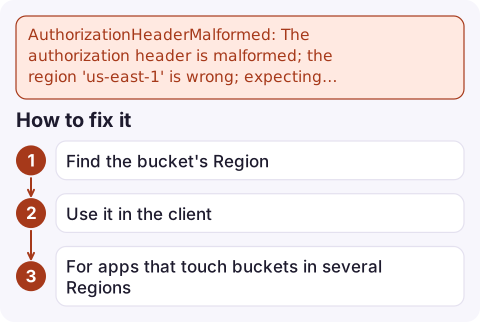
AuthorizationHeaderMalformed: the region 'us-east-1' is wrong; expecting 'eu-west-2'
Your client signed the S3 request for one Region, but the bucket lives in another. S3 tells you the right Region in the message. Configure the client (or the presigned URL generator) with the bucket's real Region, which you can read from the error itself, from aws s3api head-bucket, or from the bucket's Properties tab in the console.
What the error means
<Error>
  <Code>AuthorizationHeaderMalformed</Code>
  <Message>The authorization header is malformed; the region 'us-east-1' is wrong; expecting 'eu-west-2'</Message>
  <Region>eu-west-2</Region>
</Error>
Signature Version 4 includes the Region in the signing scope. Bucket names are global, so S3 can find the bucket wherever you send the request, but it won't accept a signature scoped to the wrong Region. The header isn't really malformed; it's signed for the wrong place.
Common causes
- The client defaults to us-east-1. A script or SDK with no Region configured, or a hard-coded
us-east-1, talking to a bucket elsewhere. - Presigned URLs generated with the wrong Region. The URL is created without error, and only fails when someone opens it.
- A bucket recreated in a different Region under the same name, while apps still carry the old Region.
- Tools that use the global endpoint (
s3.amazonaws.com) with SigV4 and a guessed Region, such as some older backup tools and S3-compatible libraries.
How to fix it
- Find the bucket's Region.
aws s3api head-bucket --bucket my-bucket --query BucketRegion --output text aws s3api get-bucket-location --bucket my-bucketget-bucket-locationreturnsnullfor us-east-1, which trips up scripts. The console shows the Region on the bucket list and under Properties. - Use it in the client:
On the CLI, adds3 = boto3.client("s3", region_name="eu-west-2") url = s3.generate_presigned_url("get_object", Params={"Bucket": "my-bucket", "Key": "reports/q3.pdf"}, ExpiresIn=900)--region eu-west-2or set it on the profile. - For apps that touch buckets in several Regions, create one client per Region, or look up the Region first with
head-bucketand cache it.
Prevent it
- Keep the bucket Region next to the bucket name in configuration, rather than relying on the process's default Region.
- Test presigned URLs in CI by fetching one, not just generating it.
- The AWS CLI's high-level
aws s3commands usually follow the redirect for you, so a script can work withaws s3 cpand still fail in your SDK code. Don't take the CLI working as proof the Region is right. - A related error, PermanentRedirect, has the same cause with a different signing path; the fix is the same.
Questions
What does AuthorizationHeaderMalformed mean in S3?
The request was signed for a different Region than the one the bucket is in. The message names the Region S3 expected.
How do I find which Region an S3 bucket is in?
Run aws s3api head-bucket --bucket NAME and read BucketRegion, or check the bucket list in the S3 console. get-bucket-location returns null for us-east-1.
Why do my S3 presigned URLs fail with AuthorizationHeaderMalformed?
The S3 client that generated them was configured for the wrong Region. Create it with the bucket's Region and generate the URL again.

Broken download links usually reach you as a support message, not an alarm. CloudConsole, a phone app for AWS, is being built to show resources and logs on your phone, which helps you check a bucket's details while you're away from your desk.
Did it start after a deploy? What changed? on the app’s alarm screen lists the deploys and configuration changes from the hour before the alarm fired.
About the app → · Download on the App Store