 CloudConsole
Amazon VPC limits and quotas
By default you get 5 VPCs, 5 Elastic IP addresses and 5 internet gateways per Region, 200 subnets and 200 route tables per VPC, 2,500 security groups per Region, 60 inbound and 60 outbound rules per security group, 5 security groups per network interface, and 20 rules per network ACL. Almost all are adjustable, but rules per security group multiplied by security groups per interface can't exceed 1,000. NAT gateways are limited to 5 per Availability Zone.
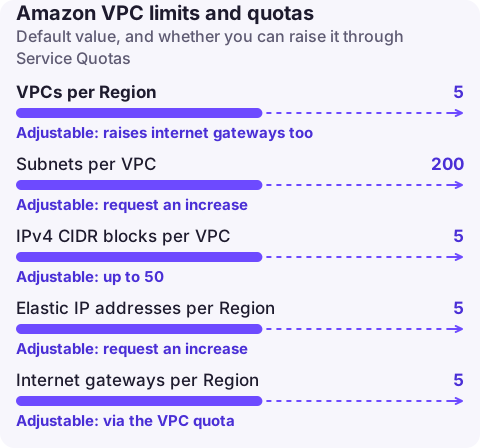
VPC, subnet and gateway quotas
| Quota | Default | Adjustable |
|---|---|---|
| VPCs per Region | 5 | Yes (raises internet gateways too) |
| Subnets per VPC | 200 | Yes |
| IPv4 CIDR blocks per VPC | 5 | Yes, up to 50 |
| Elastic IP addresses per Region | 5 | Yes |
| Internet gateways per Region | 5 | Via the VPC quota |
| Egress-only internet gateways per Region | 5 | Via the VPC quota |
| NAT gateways per Availability Zone | 5 | Yes |
| Route tables per VPC | 200 | Yes |
| Routes per route table (non-propagated) | 500 | Yes, up to 1,000 |
| Network ACLs per VPC | 200 | Yes |
| Rules per network ACL | 20 inbound and 20 outbound | Yes, up to 40 each |
| Network interfaces per Region | 5,000 (enforced per AZ) | Yes |
| Gateway VPC endpoints per Region | 20 (up to 255 per VPC) | Yes |
| Interface endpoints per VPC | 50 | Yes |
NAT gateways only count while pending, active or deleting.
Security group quotas
| Quota | Default | Adjustable |
|---|---|---|
| Security groups per Region | 2,500 | Yes |
| Inbound or outbound rules per security group | 60 | Yes |
| Security groups per network interface | 5 | Yes, up to 16 |
| Rules per group x groups per interface | 1,000 maximum | No |
Rules are counted separately for inbound and outbound, and separately for IPv4 and IPv6: a group can have 60 IPv4 inbound rules and 60 IPv6 inbound rules. A rule that references a customer-managed prefix list counts as that list's maximum entries, not its current size, so a prefix list sized for 50 entries uses 50 rules wherever it is referenced. Raising rules per group to 200 means you can attach at most 5 groups per interface (200 x 5 = 1,000), and the change applies to every network interface in the Region.
What the errors look like
RulesPerSecurityGroupLimitExceeded: The maximum number of rules per security group has been reached.SecurityGroupsPerInterfaceLimitExceededwhen attaching a sixth group.VpcLimitExceeded: The maximum number of VPCs has been reached.AddressLimitExceeded: The maximum number of addresses has been reached.for Elastic IPs.NatGatewayLimitExceededwhen creating a sixth NAT gateway in one AZ.
Check usage
# VPCs and Elastic IPs in this Region
aws ec2 describe-vpcs --query 'length(Vpcs)'
aws ec2 describe-addresses --query 'length(Addresses)'

# Inbound rule count per security group, largest first
aws ec2 describe-security-groups --query 'reverse(sort_by(SecurityGroups[].{id:GroupId,name:GroupName,inbound:length(IpPermissions)},&inbound))[:10]' --output table

# VPC quotas with codes
aws service-quotas list-service-quotas --service-code vpc --query "Quotas[].[QuotaName,QuotaCode,Value]" --output table
length(IpPermissions) counts permission entries, and one entry can hold several CIDRs or source groups, each of which is a separate rule for quota purposes; the console's rule count is the accurate one.
Designing within the limits
- Reference security groups instead of listing CIDRs: one rule allowing the load balancer's group replaces a rule per subnet. See security group rules.
- Use prefix lists for shared IP sets, sized only as large as needed.
- Prefer fewer, larger VPCs shared through AWS RAM over one VPC per team, or use Transit Gateway when you need many.
- Elastic IPs are scarce by default; NAT gateways, public load balancers and bastions all consume them. Release unattached ones, which are also billed.
Questions
How many VPCs can I create per Region?
Five by default. The quota is adjustable, and raising it also raises the internet gateway quota.
How many rules can a security group have?
60 inbound and 60 outbound by default, counted separately for IPv4 and IPv6. You can raise it as long as rules per group times groups per interface stays at or below 1,000.
How many subnets can a VPC have?
200 per VPC by default, and the quota can be increased.
VPC limits usually block a change rather than break a running system, often in the middle of a migration. CloudConsole, a phone app for AWS, is being built to show failed deployments and alarms on your phone so a blocked change doesn't go unnoticed.
About the app → · Download on the App Store