 CloudConsole
NAT gateway per Availability Zone (and the regional option)
A standard (zonal) NAT gateway lives in one Availability Zone, so if every private subnet routes through a single NAT gateway and that zone fails, all of them lose outbound internet access. The resilient zonal pattern is one NAT gateway per AZ, each in that AZ's public subnet, with each AZ's private route table pointing at its local gateway. AWS now also offers regional NAT gateways (availability mode regional) that expand across AZs automatically with one ID and no public subnet; use zonal mode for private NAT.
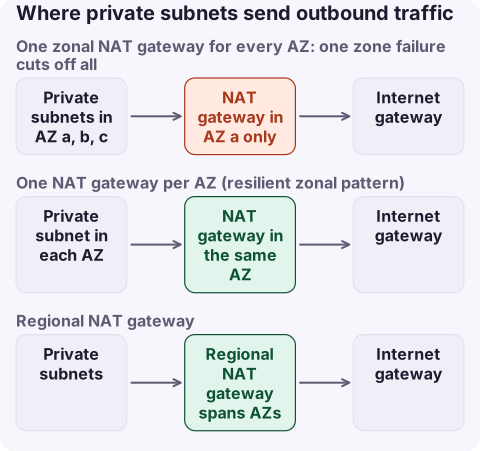
Three ways to set it up
| Design | Survives an AZ outage? | Cost | Management |
|---|---|---|---|
| One zonal NAT gateway for the whole VPC | No: all private subnets lose egress | One hourly charge; cross-AZ data transfer for other AZs | Simple |
| One zonal NAT gateway per AZ, per-AZ route tables | Yes: other AZs keep working | One hourly charge per AZ | Route table per AZ; update when adding AZs |
| One regional NAT gateway | Yes: it keeps zonal affinity and expands to AZs with workloads | See VPC pricing | One ID and one route for all subnets; no public subnet |
A zonal NAT gateway is redundant inside its own AZ, but not beyond it. Routing every AZ through one gateway also adds cross-AZ data transfer charges for traffic from the other AZs.
Zonal: one per AZ
For each AZ: an Elastic IP, a NAT gateway in that AZ's public subnet, and a private route table with 0.0.0.0/0 pointing to it.
aws ec2 allocate-address --domain vpc
aws ec2 create-nat-gateway --subnet-id subnet-0aaa1111bbbb2222c --allocation-id eipalloc-0123456789abcdef0 \
  --tag-specifications 'ResourceType=natgateway,Tags=[{Key=Name,Value=nat-eu-west-2a}]'
aws ec2 create-route --route-table-id rtb-0private2a000000 --destination-cidr-block 0.0.0.0/0 \
  --nat-gateway-id nat-0123456789abcdef0
Repeat for each AZ. In Terraform, that means one aws_nat_gateway per public subnet and one private route table per AZ.
Regional: one gateway across AZs
aws ec2 create-nat-gateway --vpc-id vpc-0a1b2c3d4e5f67890 --availability-mode regionalIn automatic mode AWS manages the IP addresses and expands the gateway into an AZ when it detects network interfaces there (this can take up to 60 minutes; until then traffic from the new AZ is processed in an existing one) and contracts when the AZ is empty. Manual mode lets you assign Elastic IPs per AZ. Each AZ can use up to 32 IP addresses, against 8 for a zonal gateway. Regional NAT gateways don't support private connectivity and aren't available in constrained AZs. Converting from zonal resets existing connections.
CloudFormation: AWS::EC2::NatGateway with AvailabilityMode (zonal or regional), VpcId and optional AvailabilityZoneAddresses for regional; SubnetId and AllocationId for zonal. Terraform: aws_nat_gateway with availability_mode (default zonal), vpc_id and availability_zone_address blocks for regional; subnet_id and allocation_id for zonal.
Capacity facts that matter
- A zonal NAT gateway starts at 5 Gbps and scales to 100 Gbps, and up to 10 million packets per second.
- Each IP address supports up to 55,000 simultaneous connections to a single destination (IP, port, protocol). Exhaustion shows up as
ErrorPortAllocation; add secondary IPs or spread traffic. See the port allocation alarm. - Quota: 5 NAT gateways per AZ by default.
Reducing NAT cost without losing resilience
- Add gateway endpoints for S3 and DynamoDB so that traffic skips NAT entirely.
- Use interface endpoints for chatty AWS APIs (ECR, CloudWatch Logs, STS) when their volume justifies it.
- For non-production VPCs, one NAT gateway is often acceptable; just know what an AZ outage does.
Questions
Do I need a NAT gateway in every Availability Zone?
For zonal NAT gateways, yes if you want private subnets in each AZ to keep internet access when another AZ fails. A regional NAT gateway gives multi-AZ coverage with a single gateway.
What is a regional NAT gateway?
A NAT gateway created with availability mode regional. It spans the VPC's Availability Zones, expands and contracts with your workloads, uses one route entry for all subnets and needs no public subnet. It doesn't support private NAT.
Is one NAT gateway per AZ more expensive?
Yes, each gateway has an hourly charge. Sharing one gateway saves that but adds cross-AZ data transfer and removes resilience to an AZ failure.
An AZ problem that takes out a shared NAT gateway looks like a total outage of everything private. CloudConsole, a phone app for AWS, is being built to show NAT gateway and application alarms on your phone.
About the app → · Download on the App Store