 CloudConsole
VPC gateway endpoints for S3 and DynamoDB
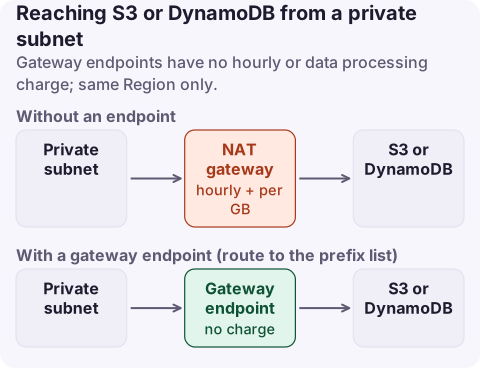
A gateway VPC endpoint lets resources in a VPC reach S3 or DynamoDB in the same Region without an internet gateway or NAT, and it has no hourly or data processing charge. You attach it to route tables, and AWS adds a route to the service's prefix list for every subnet using those tables. It doesn't work from on-premises, peered VPCs in other Regions or through Transit Gateway (use interface endpoints there). Almost every VPC with private subnets should have both gateway endpoints, because NAT gateway data processing for S3 traffic is a common avoidable cost.
Gateway vs interface endpoints for S3
| Gateway endpoint | Interface endpoint (PrivateLink) | |
|---|---|---|
| Services | S3 and DynamoDB only | S3, DynamoDB and most AWS services |
| Cost | Free | Hourly per AZ plus per GB |
| How traffic finds it | Route table entry to a prefix list | Private IPs and DNS in your subnets |
| From on-premises, other-Region peering, Transit Gateway | No | Yes |
| Security groups | Not applicable (instances' own SGs apply) | Yes, on the endpoint |
| Quota | 20 per Region, up to 255 per VPC | 50 per VPC |
Use gateway endpoints for traffic from inside the VPC, and add interface endpoints only where you need access from outside it.
Set it up
aws ec2 create-vpc-endpoint --vpc-id vpc-0a1b2c3d4e5f67890 --vpc-endpoint-type Gateway \
  --service-name com.amazonaws.eu-west-2.s3 \
  --route-table-ids rtb-0123456789abcdef0 rtb-0fedcba9876543210

aws ec2 create-vpc-endpoint --vpc-id vpc-0a1b2c3d4e5f67890 --vpc-endpoint-type Gateway \
  --service-name com.amazonaws.eu-west-2.dynamodb \
  --route-table-ids rtb-0123456789abcdef0 rtb-0fedcba9876543210

# Confirm the prefix-list routes were added
aws ec2 describe-route-tables --route-table-ids rtb-0123456789abcdef0 \
  --query 'RouteTables[0].Routes[?DestinationPrefixListId].[DestinationPrefixListId,GatewayId]'
Associate every route table used by private subnets (and public ones too if instances there talk to S3). CloudFormation: AWS::EC2::VPCEndpoint with VpcEndpointType: Gateway, ServiceName, VpcId, RouteTableIds and optional PolicyDocument. Terraform: aws_vpc_endpoint with vpc_endpoint_type = "Gateway", service_name, vpc_id and route_table_ids.
Policies and conditions
- The endpoint policy defaults to full access. Restrict it to your buckets (and the AWS-owned buckets your instances need, such as package repositories and SSM) to stop data being copied to someone else's bucket.
- Bucket policies can require the endpoint with
aws:SourceVpceor the VPC withaws:SourceVpc. Requests via the endpoint arrive from private addresses, soaws:SourceIpconditions with public IPs no longer match; useaws:VpcSourceIpfor private IP conditions. - Security groups with restricted egress must allow HTTPS to the service's prefix list (for example
pl-ID for S3) rather than to CIDRs.
Things to know before you add one
- Creating or modifying an endpoint switches routes and resets open TCP connections to S3 from affected subnets. Do it when long transfers aren't running, or make sure clients reconnect.
- It only covers buckets in the same Region. Traffic to buckets elsewhere still goes through NAT or the internet gateway.
- With the Amazon DNS server you need DNS resolution and DNS hostnames enabled on the VPC.
- One route table can't have two endpoint routes for the same service.
Symptoms of problems
| Symptom | Cause |
|---|---|
AccessDenied from S3 right after adding the endpoint | Bucket policy with aws:SourceIp, or a restrictive endpoint policy |
| S3 calls from one subnet still use NAT | That subnet's route table isn't associated |
| Timeouts to S3 | Security group or NACL egress blocks the prefix list ranges |
| NAT data processing still high | Traffic to other-Region buckets or to other services; check flow logs |
Questions
Is a VPC gateway endpoint free?
Yes. Gateway endpoints for S3 and DynamoDB have no hourly or data processing charges. Interface endpoints are charged.
Should I use a gateway or interface endpoint for S3?
Use a gateway endpoint for traffic from inside the VPC. Use an interface endpoint when you need access from on-premises, from peered VPCs in other Regions or through Transit Gateway.
Does a DynamoDB VPC endpoint need a policy?
No, the default policy allows full access, but restricting it to your tables is good practice.
Endpoint changes can break S3 access for a whole subnet at once. CloudConsole, a phone app for AWS, is being built to show error alarms on your phone so a broken route or policy is noticed fast.
About the app → · Download on the App Store